Post-Quantum Cryptography: The Encryption Revolution We Need
Exploring the urgent need for post-quantum cryptography as quantum computing threatens to break current encryption methods, with practical steps for upgrading security standards.

Post-quantum cryptography (PQC) represents one of the most critical security challenges of our era. As quantum computing advances toward breaking classical encryption like RSA and ECC, organizations must begin transitioning to quantum-resistant algorithms now. This article explores the quantum threat, PQC approaches, and practical steps for securing digital infrastructure against future quantum attacks.
Why Does Post-Quantum Cryptography Matter?
Post-quantum cryptography matters because quantum computers will eventually break current encryption standards like RSA and ECC, threatening everything from online banking to government communications. NIST has already begun standardizing PQC algorithms, making this a present-day priority for organizations handling sensitive data.
Sources: NIST Post-Quantum Cryptography Standardization
What if I told you that the very foundation of digital security is about to face its greatest challenge in history?
In a world where our daily transactions, communications, and data are protected by cryptographic algorithms that have served us well for decades, a new threat is emerging that could render our current encryption methods obsolete. This isn't science fiction—it's the reality of post-quantum cryptography (PQC), and it's time we understand why this transition is not just necessary but urgent.

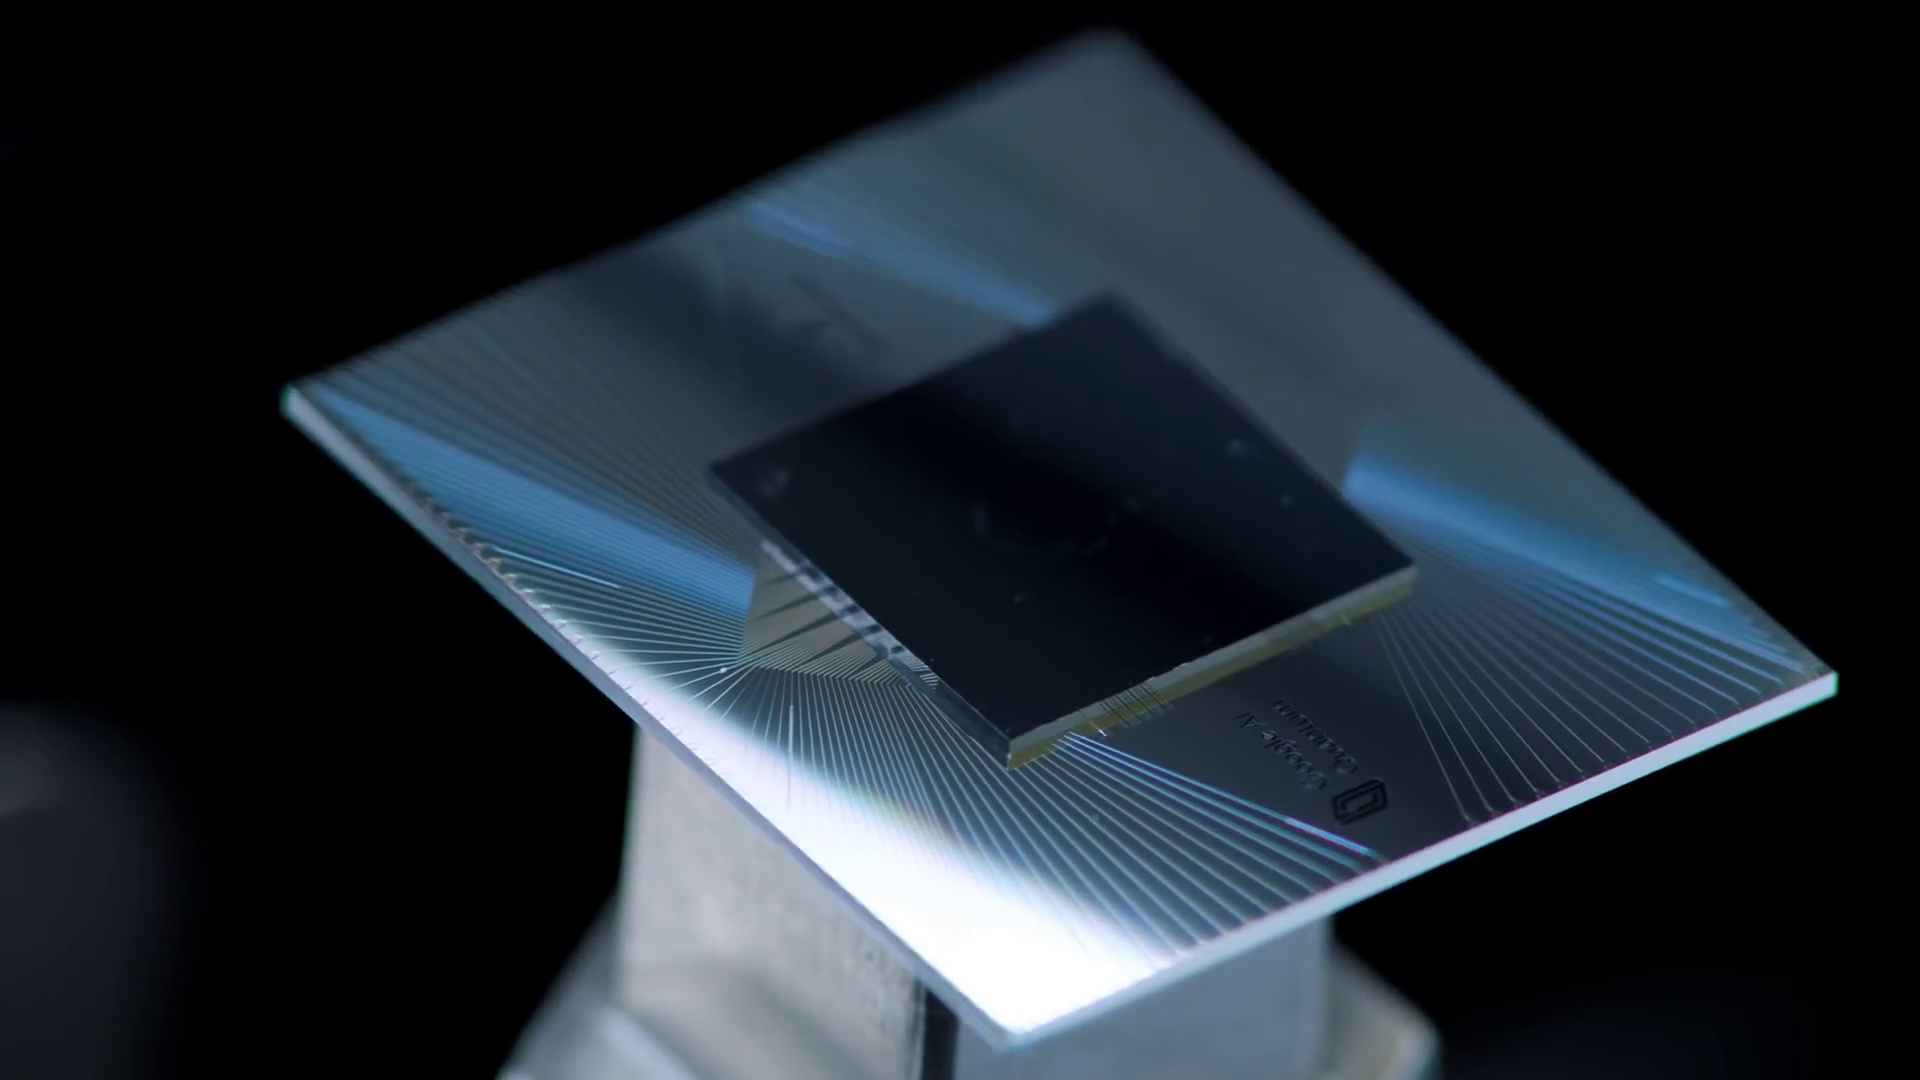
Image: Conceptual representation of quantum computing and its potential impact on cryptography
The Quantum Threat to Current Encryption
Current encryption systems like RSA and ECC (Elliptic Curve Cryptography) rely on mathematical problems that are computationally difficult for classical computers to solve. However, quantum computers—particularly those using Shor's algorithm—can theoretically solve these problems exponentially faster.
This creates a critical vulnerability: once sufficiently powerful quantum computers become available (potentially within the next 10-20 years), they could break the encryption that secures everything from online banking to secure messaging, government communications, and even our digital identities.
The implications are staggering. Our entire digital infrastructure, built on assumptions about computational difficulty, would suddenly become vulnerable to attacks that could compromise sensitive data at scale.
What is Post-Quantum Cryptography?
Post-quantum cryptography refers to cryptographic algorithms that are designed to be secure against both classical and quantum computers. These algorithms are based on mathematical problems that quantum computers cannot efficiently solve, providing long-term security guarantees even in a quantum computing world.
The National Institute of Standards and Technology (NIST) has been leading the standardization effort for PQC algorithms, with several promising candidates emerging from various research approaches:
Lattice-Based Cryptography
Based on the hardness of problems related to lattices in mathematics. This approach offers strong security guarantees and is particularly well-suited for key exchange and digital signatures.
Hash-Based Signatures
Utilizes cryptographic hash functions to create digital signatures that are resistant to quantum attacks while maintaining simplicity and efficiency.
Code-Based Cryptography
Relies on the difficulty of decoding random linear codes, offering robust security with potentially efficient implementations.
Multivariate Cryptography
Uses systems of multivariate polynomial equations for cryptographic applications, providing an alternative approach to traditional number theory-based methods.
Why This Matters Now
The transition to post-quantum cryptography isn't just about preparing for a future threat—it's about ensuring we don't lose our security infrastructure in the transition period. As quantum computing technology advances, organizations must begin implementing PQC solutions before quantum computers can break current systems.
This means that:
- Security is not optional - Any organization handling sensitive data needs to start planning now
- The transition period is critical - We need to implement new systems without creating security gaps
- Compatibility matters - New algorithms must work seamlessly with existing infrastructure
- Performance considerations - PQC algorithms often require more computational resources
The Path Forward: Uplifting Current Encryption Standards
Rather than simply replacing our current encryption methods, we should be thinking about how to uplift our entire cryptographic ecosystem:
1. Hybrid Approaches
Implementing hybrid solutions that combine classical and post-quantum algorithms provides immediate security while preparing for the quantum future. This approach allows organizations to gradually transition without disrupting current operations.
2. Gradual Migration Strategies
Developing comprehensive migration plans that address:
- Key management changes
- Infrastructure updates
- Performance impact assessments
- Integration with existing systems
3. Standards and Governance
Establishing clear governance frameworks for PQC implementation, including:
- Algorithm selection criteria
- Implementation guidelines
- Security audit processes
- Continuous monitoring protocols
Real-World Applications and Examples
Several organizations are already beginning this transition:
- Financial Institutions: Banks are implementing hybrid cryptographic solutions to protect sensitive transactions
- Healthcare Organizations: Medical institutions are updating encryption for patient data protection
- Government Agencies: Defense and intelligence organizations are preparing for quantum-resistant communications
- Technology Companies: Major cloud providers are integrating PQC into their infrastructure
The Call to Action: Securing Our Digital Future
The shift to post-quantum cryptography is not just a technical challenge—it's a strategic imperative. Every organization that handles sensitive data, from small businesses to global enterprises, must begin planning its quantum-safe transition today.
Here's what you can do now:
- Assess your current cryptographic infrastructure - Identify where your encryption is used and what systems are vulnerable
- Research PQC algorithms - Understand which approaches align with your specific needs
- Develop a transition timeline - Create a realistic roadmap for implementation
- Start small, scale gradually - Begin with high-value applications before expanding to your entire infrastructure
- Stay informed - Monitor NIST standardization efforts and emerging best practices
The clock is ticking, but the good news is that we're not starting from scratch. We have a robust foundation of cryptographic research, and we're already seeing practical implementations. The question isn't whether quantum computing will break current encryption—it's how quickly we can transition to quantum-safe solutions.
This isn't about fear—it's about proactive preparation. The future of digital security depends on our willingness to uplift current encryption standards with quantum-resistant approaches now, rather than waiting until it's too late.
The next decade will define the security landscape for generations to come. Are you ready to be part of the solution that protects our digital future?
Image source: Conceptual representation of quantum computing and its potential impact on cryptography by User:QuantumComputingFan (Own work) CC BY-SA 4.0, via Wikimedia Commons
Would you like me to help you implement any specific aspects of post-quantum cryptography in your current infrastructure or research projects?
Feature image: Google ( https://www.youtube.com/channel/UCK8sQmJBp8GCxrOtXWBpyEA ) / CC BY 3.0 / Wikimedia Commons.
